
Executive Summary & Key Takeaways
Key Insights- Governance must be operational, not only documented; risk tiers should determine review depth; evaluation should drive release decisions; least-privilege access reduces blast radius; production monitoring and incident learning are lifecycle controls; NIST AI RMF and ISO/IEC 42001 can provide complementary foundations.
Quick Definition / Direct Answer
Direct SummaryAn enterprise AI governance framework connects business ownership, risk classification, security, evaluation, release approval, production monitoring, and audit evidence across the lifecycle of AI systems.
Executive Summary
Enterprise AI governance is not a policy document alone. It is the operating system for deciding which intelligent systems may be built, how risks are assessed, what evidence is required before release, who can approve, restrict, or stop deployment, and how production behavior is monitored.
This white paper presents a practical governance model that connects business ownership, risk management, evaluation, security, deployment controls, observability, incident response, and audit evidence.
1. Why Enterprise AI Governance Needs an Operating Model
Organizations often begin with separate activities: a security review, model evaluation, privacy checklist, or architecture approval. The weakness is fragmentation. A production governance model should connect these activities into one decision path.
Need AI or Software Engineering Support?
Turn your ideas and technical challenges into reliable, scalable solutions with Acadify. From AI development and automation to software engineering and product development, we help businesses build and grow with confidence.
- What system is being built or acquired?
- What business and technical risks does it introduce?
- What evidence is required before release?
- Who can approve, restrict, or stop it?
- What changes after deployment and how are they detected?
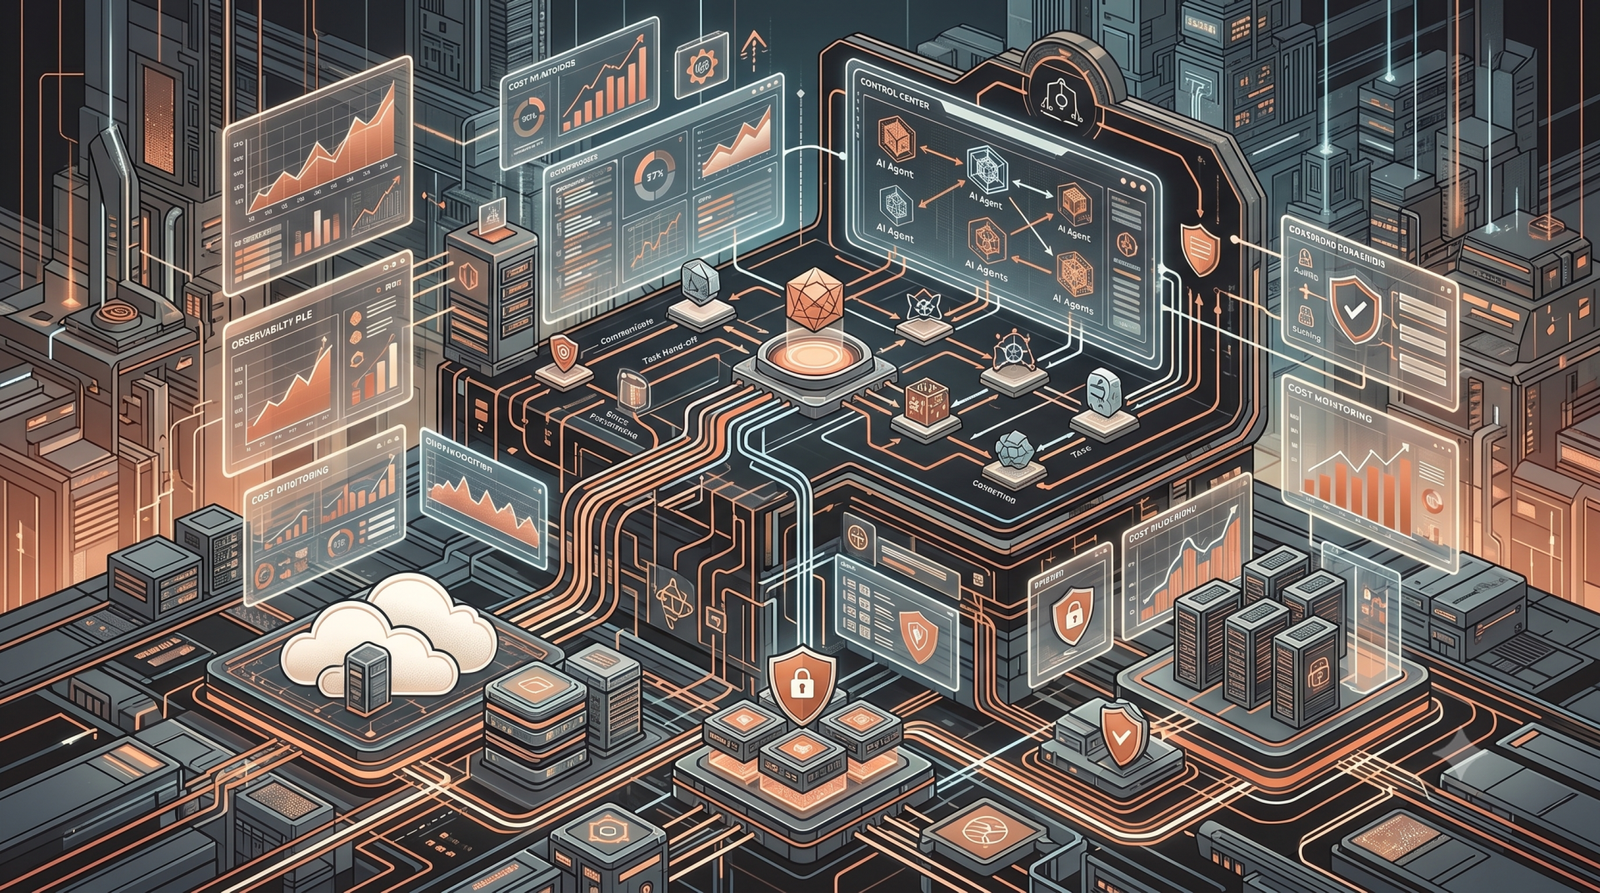
2. A Reference Governance Architecture
Business objective
      ↓
System inventory and ownership
      ↓
Risk classification
      ↓
Security + privacy assessment
      ↓
Evaluation and validation
      ↓
Release decision
      ↓
Production controls
      ↓
Continuous monitoring
      ↓
Incident response + change review
      ↓
Governance evidence and audit trail
The key design principle is traceability. Important decisions should connect to an owner, risk statement, evidence, approval state, and review trigger.
3. Governance Foundations
3.1 System inventory
Maintain a system register covering models, applications, agents, retrieval pipelines, external providers, high-impact workflows, and major changes. Record business and technical owners, data classes, dependencies, deployment environment, intended use, and prohibited use.
3.2 Risk classification
Use a risk tier that determines the depth of review. A low-impact internal assistant should not require the same control burden as a system that triggers consequential business actions.
| Tier | Typical characteristics | Governance expectation |
|---|---|---|
| Low | Internal productivity, low-impact assistance | Basic security, owner, evaluation, monitoring |
| Moderate | Customer-facing or business-critical workflows | Structured evaluation, security review, release gates, incident process |
| High | Material financial, legal, safety, privacy, or operational impact | Enhanced validation, explicit approval, stronger monitoring, documented controls |
3.3 Accountability
Governance fails when responsibility is shared by everyone and owned by no one. Assign accountable business and technical owners, with escalation authority for security, privacy, compliance, and production incidents.
4. Mapping Governance to the AI Lifecycle
NIST describes the AI Risk Management Framework as a way to incorporate trustworthiness into the design, development, use, and evaluation of AI systems. Its Generative AI Profile extends the framework with risks and suggested actions specific to generative systems.
| Lifecycle stage | Governance questions | Required evidence |
|---|---|---|
| Plan | Why is the system needed? Who owns it? | Business case, scope, intended use |
| Design | What data, models, tools, and permissions are involved? | Architecture, threat model, data map |
| Build | How is quality measured? | Evaluation dataset, test results, version history |
| Release | Has the system met its thresholds? | Release decision, security and evaluation evidence |
| Operate | What can change after deployment? | Monitoring, logs, incident records |
| Review | When must the system be reassessed? | Periodic review, material-change triggers |
5. Evaluation as a Governance Control
Evaluation should produce decision evidence, not only a benchmark score. Define representative tasks, expected outcomes, failure categories, thresholds, and an owner for reviewing results.
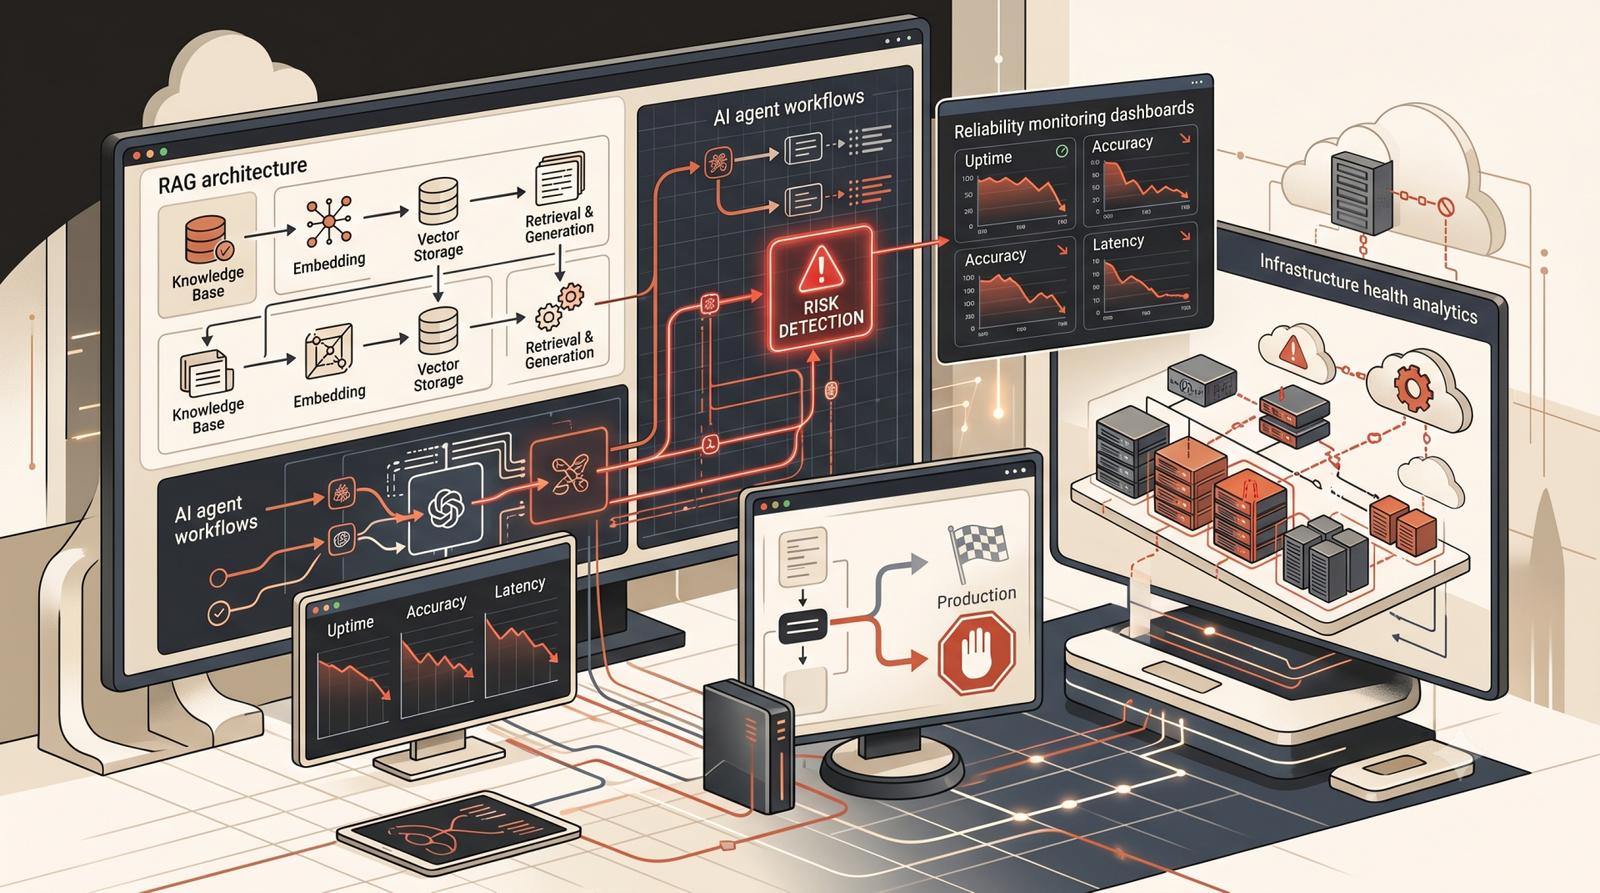
For systems that use retrieval, tools, or agents, evaluate the workflow as a system. Evidence can include task success, groundedness, retrieval quality, tool-call correctness, refusal behavior, policy adherence, latency, and regression results.
if critical_failures > 0:
    block_release()

elif security_review != "approved":
    block_release()

elif evaluation_score < threshold:
    require_remediation()

else:
    approve_release()
6. Security and Access Controls
Security governance should cover the full application path, not only the underlying model. Review authentication, authorization, secrets, data handling, prompt injection exposure, tool permissions, external integrations, logging, and isolation boundaries.
For agentic workflows, least privilege is essential. Each tool should have a narrow purpose, explicit inputs, bounded permissions, and a traceable identity. High-impact actions may require human confirmation or additional policy checks.
7. Privacy and Data Governance
Identify what information enters prompts, retrieval indexes, logs, training or fine-tuning workflows, and third-party services. Retention, access, deletion, residency, and permitted-use policies should be defined for each relevant data class.
Provider security documentation does not by itself establish application compliance. Organizations remain responsible for their application architecture, access controls, data flows, contracts, and operational practices.
8. Governance Standards and Regulatory Alignment
8.1 NIST AI RMF
The NIST AI RMF is intended for voluntary use and provides a framework for managing risks associated with AI. NIST's Generative AI Profile identifies risks that are novel to or amplified by generative systems and provides suggested actions across the lifecycle.
8.2 ISO/IEC 42001
ISO/IEC 42001:2023 specifies requirements for establishing, implementing, maintaining, and continually improving an Artificial Intelligence Management System (AIMS). It provides organizational management-system structure rather than a substitute for technical testing.
8.3 Regulatory requirements
Organizations should map applicable legal requirements to system use cases, geography, data categories, and impact. Governance should support compliance work without treating a single framework as universal legal advice.
9. Evidence and Auditability
An effective governance program creates an evidence trail. For each governed system, retain the records needed to reconstruct key decisions.
- System and model inventory
- Risk classification and ownership
- Architecture and data-flow records
- Threat and security assessments
- Evaluation datasets and results
- Release approvals and exceptions
- Monitoring and incident records
- Material-change and review history
10. Operating Model for Enterprise Teams
| Role | Primary responsibility |
|---|---|
| Business owner | Purpose, value, acceptable risk, business approval |
| Technical owner | Architecture, implementation, reliability and operations |
| Security | Threat modeling, access controls, security validation |
| Privacy / compliance | Data controls and applicable obligations |
| Evaluation owner | Datasets, metrics, graders, release evidence |
| Operations | Monitoring, incident response, rollback and change management |
11. Common Governance Failure Modes
Policy without enforcement
A written policy cannot prevent unsafe deployment unless it is connected to technical gates and accountable approvals.
One-time assessment
Model, prompt, retrieval, data, tools, and application behavior can change. Governance should include review triggers and ongoing monitoring.
Benchmark-only evaluation
A benchmark can miss domain-specific failures. Representative production tasks and failure analysis are more useful for operational decisions.
Unbounded permissions
Granting an agent broad access increases blast radius. Scope tools and credentials to the minimum required action.
Missing evidence
If decisions are not recorded, teams may be unable to explain why a system was approved, what was tested, or which exceptions remain open.
12. Enterprise Governance Maturity Model
| Level | Characteristics |
|---|---|
| 1 — Ad hoc | Individual teams make isolated decisions with limited evidence. |
| 2 — Documented | Policies and basic review processes exist. |
| 3 — Controlled | Risk tiers, evaluation gates, ownership, and monitoring are operational. |
| 4 — Measured | Governance uses metrics, audit evidence, incident learning, and systematic reassessment. |
| 5 — Adaptive | Controls evolve from production evidence, changing risks, and material system changes. |
13. Practical Implementation Roadmap
Phase 1 — Establish the inventory
Identify systems, owners, providers, data classes, deployment environments, and business impact.
Phase 2 — Define risk tiers
Create consistent criteria and map each tier to required evidence, reviewers, approval authority, and review frequency.
Phase 3 — Operationalize evaluation
Build representative datasets, define metrics and thresholds, and connect results to release decisions.
Phase 4 — Enforce security and access boundaries
Implement least privilege, threat testing, logging, secrets management, and human approval for high-impact actions.
Phase 5 — Monitor production
Collect traces and quality signals, detect material changes, and feed incidents back into evaluation and governance.
Phase 6 — Audit and improve
Review evidence, exceptions, incidents, and control performance. Update policies and technical controls when system behavior or obligations change.
14. Governance Readiness Checklist
- Business and technical owners are assigned.
- The system is recorded in an inventory.
- Risk tier and intended use are documented.
- Security and privacy reviews are complete.
- Representative evaluations exist.
- Release thresholds are defined.
- Tool and data permissions are bounded.
- Monitoring and incident response are operational.
- Material-change triggers are defined.
- Approval and exception evidence is retained.
15. Conclusion
Enterprise governance works when policies become operational controls. The strongest model connects risk classification, security, evaluation, release gates, deployment restrictions, observability, incident response, and evidence into one lifecycle.
NIST provides a risk-management foundation, while ISO/IEC 42001 provides an organizational management-system structure. Organizations should adapt these resources to their own risk profile, systems, contractual obligations, and applicable law.
Frequently Asked Questions
What is an enterprise AI governance framework?
It is a set of policies, roles, processes, technical controls, evaluations, approvals, and monitoring practices used to manage the risks and responsibilities associated with AI systems across their lifecycle.
Is NIST AI RMF a certification standard?
No. NIST describes the AI RMF as a voluntary framework for managing AI risks.
What is ISO/IEC 42001?
ISO/IEC 42001:2023 is an international standard specifying requirements for an Artificial Intelligence Management System.
When should an AI system be reassessed?
Reassessment should be triggered by material changes such as a new model, major prompt or retrieval changes, new tools or permissions, significant data changes, changes in intended use, serious incidents, or applicable regulatory changes.
About Acadify Solution
Acadify Solution works on enterprise software, AI engineering, evaluation, reliability, security, deployment, and production-readiness initiatives. This white paper is a practical engineering and governance reference, not legal advice or a statement of certification.
Related Technical Reading: Explore our in-depth architecture guide on Enterprise AI Operating Model: Roles, Controls, Evaluation & Production Lifecycle.
Related Technical Reading: Explore our in-depth architecture guide on Cloud-Native Enterprise AI Model Serving & SLOs.
Glossary & Key Architecture Definitions
- • Enterprise AI governance: the policies, roles, processes, technical controls, evaluations, approvals, and monitoring used to manage AI systems across their lifecycle. AI Risk Management Framework: a NIST framework for managing AI risks. AIMS: an Artificial Intelligence Management System specified by ISO/IEC 42001. Release gate: a defined condition that determines whether a system may proceed to deployment.
Engineering Research & Citations
- [1] NIST AI Risk Management Framework: https://www.nist.gov/itl/ai-risk-management-framework; NIST AI RMF Generative AI Profile: https://www.nist.gov/publications/artificial-intelligence-risk-management-framework-generative-artificial-intelligence; ISO/IEC 42001:2023: https://www.iso.org/standard/42001
No perspectives submitted yet. Be the first to start the discussion.